Serpent Cipher Explained: How It Works, With Code in C, C++, Java, Python and C#
The AES finalist with a 32-round safety margin: how Serpent works, why two correct versions disagree, and four mistakes that a round-trip test misses.
The AES finalist with a 32-round safety margin: how Serpent works, why two correct versions disagree, and four mistakes that a round-trip test misses.
When it comes to DevOps, there’s a lot of hype. But what does it mean for your organization? More importantly, how can you make sure that the DevOps service provider you choose is the right one for your unique needs? Here are some quick tips on how to find the best partner for your organization:
PVS-Studio is a commercial static code analyzer developed by PVS-Studio LLC. It is designed to help software developers detect errors and potential vulnerabilities in their code by analyzing it without actually running it. The tool supports several programming languages: C, C++, C#, and Java. This makes it a versatile option for teams working on projects with different language requirements.
Malicious hackers constantly look for vulnerabilities to exploit and sensitive data to steal. The consequences of a successful hack can be severe, not only for users but also for the developers of the affected app. A data breach can lead to loss of revenue, damage to reputation, and even legal action. Therefore, it is crucial for app developers to take proactive steps to safeguard their creations and the sensitive data they handle. This article has some essential tips to help you secure your app development process like a pro.
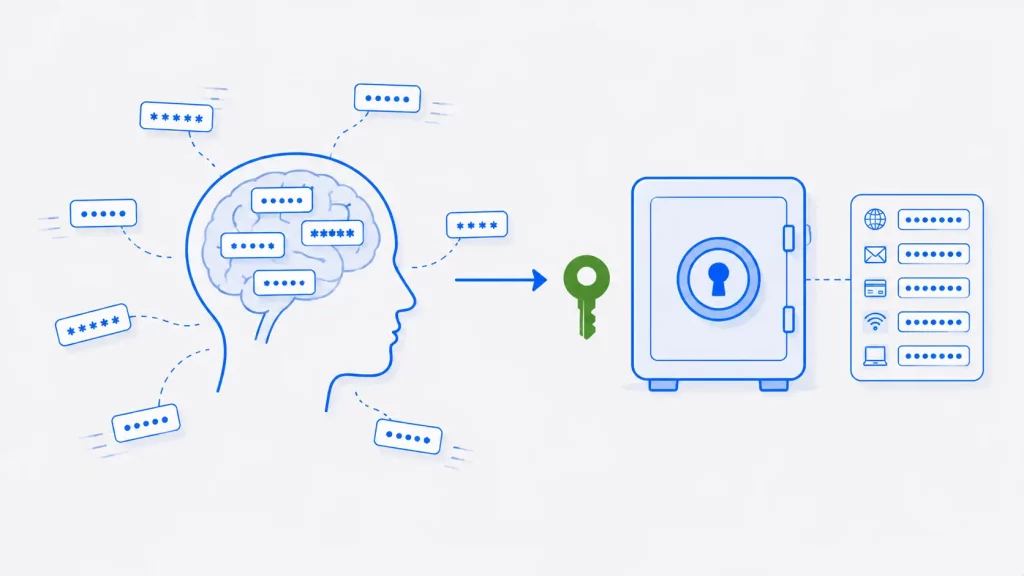
The average person juggles over 100 passwords, so forgetting them is inevitable. Here’s the psychology behind why we forget passwords — and the modern tools that fix it for good.
Dynamic ARP Inspection a security feature that helps mitigate attacks that use spoofed Address Resolution Protocol (ARP) packets. Dynamic ARP inspection works by verifying that all ARP traffic on a network is valid. Invalid ARP packets are dropped, which helps protect your network from attacks that use forged or spoofed source IP addresses.
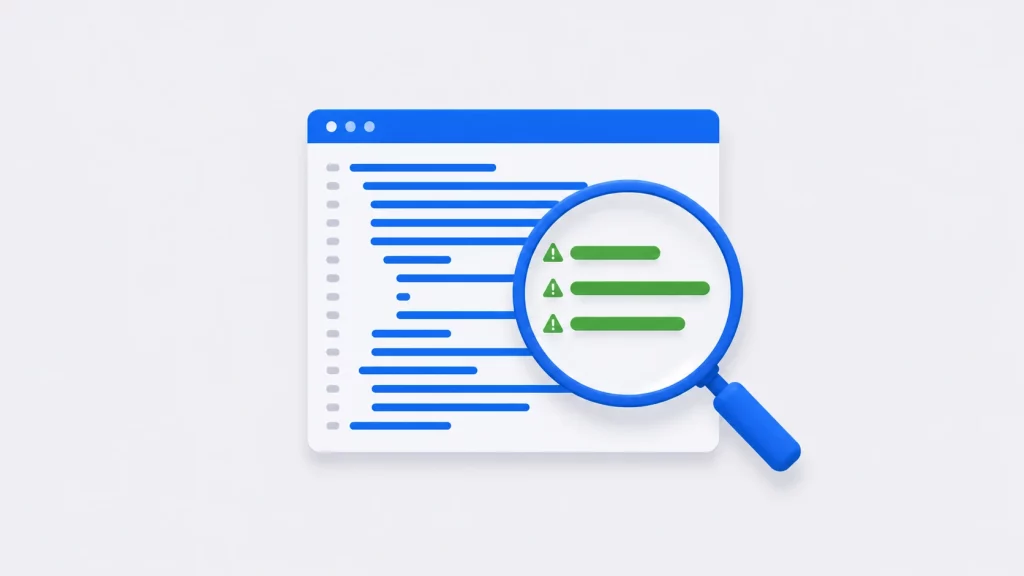
A comparison of 12 static analysis tools, anchored by a hands-on test showing no single analyzer found more than five of eight planted defects.
One of the primary regulatory standards that merchants should abide by is the PCI DSS. The Payment Card Industry Data Security Standard (PCI DSS) is a set of requirements that cater towards protecting consumers and their data as they make transactions using their cards.
Choosing the right backup software is crucial as it is your important files and data you’re protecting. It should have the features that you need as well, to get your money’s worth. Yet, it can be so hard to choose a backup software with so many options to choose from in the market. To help you find the best one for you, here are some questions you should ask.
Three centuries as the indecipherable cipher, and 1.6 milliseconds to break. Working C++ for both directions, plus the attack that recovers the key.
The other name for RASP is Runtime Application Self Protection. It is one of the most contemporary technicalities that help in protecting the running application in time. It can be compared to WAF perimetral approach and RAASP helps in protecting the applications from the interior. It refers that RASP has greater visibility in case of data flow and each input comes with the consequences to help the application receive with glee. Here is the post to describe the perfect working of RASP along with the set of necessary advantage. This will help compare the perimetral defenses and this can be leveraged by the main teams as part of the Software Development Lifecycle.
Why == silently fails on C strings, how to read strcmp’s return value correctly, and the safe input pattern the comparison depends on.